OneVision
Transmission towers at dusk overlaid with threat-alert text — firewall disabled, virus detected, cyber attack — and scattered data characters
Exposure & resilience

Your perimeter ended at the substation fence.

Remote sites, plant floors, and vendor connections widen the attack surface faster than any tool catalog closes it. We map what is actually exposed, then rank it by what an hour of downtime costs you.

How we engage

Frameworks and standards we assess, remediate, and report against

SOC 2HITRUSTHIPAAGLBACJISFFIECNIST CSFISO 27001FedRAMPNIST 800-171CMMC
Cybersecurity · vCISO · Compliance

Executive-grade cybersecurity for organizations that can’t afford to get it wrong.

Strategic security leadership delivered as a service — the accountability of a full-time CISO, a purpose-built platform behind them, and risk stated in the terms your board already decides in.

01

The practice

A security partner, not a product pitch

We provide executive-level security leadership, regulatory compliance, and risk-based assurance to organizations operating under real scrutiny.

Most firms sell you a scan and a stack of findings. We operate as your security leadership: we set the strategy, run the assessment, close the gaps, and stand behind the posture in front of your board, your auditors, and your customers.

What that looks like

  • Strategy set by a practicing vCISO
  • One pass across three frameworks
  • Risk quantified in dollars, not colors
  • Reporting built for the boardroom
02

Professional services

Three ways we engage

A backlit CISO module on a circuit board, lit in blue and copper

Virtual CISO Advisory

Executive security leadership delivered as a service — the accountability of a full-time CISO without the full-time cost.

  • Program strategy & governance
  • Board-ready reporting
  • Policy & standards ownership
A hand working a holographic risk dashboard, the risk-management dial reading between low and high

Risk Assessment & Compliance

Risk-based assessments that rank real business exposure and map cleanly to the frameworks your regulators and customers expect.

  • Gap & maturity assessments
  • Audit & exam readiness
  • Third-party risk reviews
A security consultant working through a lit control dashboard on a wall display, phone in hand

Cybersecurity Professional Services

Hands-on delivery to close the gaps the assessment finds — control implementation, remediation, and managed operation.

  • Control implementation
  • Remediation project management
  • Managed security services
03

What is at stake

A breach does not send one invoice

The ransom, if there is one, is the smallest line. The rest arrives in pieces over the months that follow — from counsel, from the regulator, from customers re-reading their contracts, and from the revenue that never showed up while the plant was down.

The line stops

Production halted, orders unshipped, and staff idle while systems are rebuilt from the last known-good copy — revenue that is not deferred, just gone.

The response is not budgeted

Forensics, outside counsel, notification, credit monitoring, and overtime for every team pulled off its roadmap to work the incident.

The regulator arrives after

Statutory notification clocks, examination findings, and penalties that outlast the outage by years — assessed on the evidence you can produce, not the effort you describe.

Every customer re-underwrites you

Security reviews reopened, insurers tightening terms at renewal, and pipeline that stalls until someone can answer for the controls in writing.

None of those lines are reduced by a certificate on the wall. They are reduced by controls that work on an ordinary Tuesday — which is what the rest of this page is about.

04

The platform

Most GRC tools stop at the checklist. Ours starts there.

A control library, an audit trail, and a dashboard describing where you stood last quarter is where most platforms finish. It is where ours begins.

A unified control framework harmonizes more than 200 controls across nine leading standards, so one assessment answers every framework at once — no duplicate evidence gathering, no audit fatigue. Risk is not scored on gut-feel heat maps; it is quantified with a defensible, financially grounded method that turns control gaps into dollars, so boards prioritize security investment with the rigor they apply to any other decision.

Continuous exposure monitoring, supplier assessments, breach surveillance, and live intelligence feeds keep the picture current in real time rather than frozen at the last audit. Remediation guidance is attached to every control, so findings become work instead of shelf-ware. Service management, incident tracking, project and budget management, and policy generation connect governance to execution — the gap where most programs quietly fail. Automated evidence collection, scheduled assessments, and role-based workflows mean the program runs itself between audits instead of being rebuilt for each one.
One assessment, nine frameworks

201

Harmonized controls

17

Control domains

9

Frameworks, one pass

6

Security functions

NIST CSFISO 27001CIS ControlsCMMC+ five more
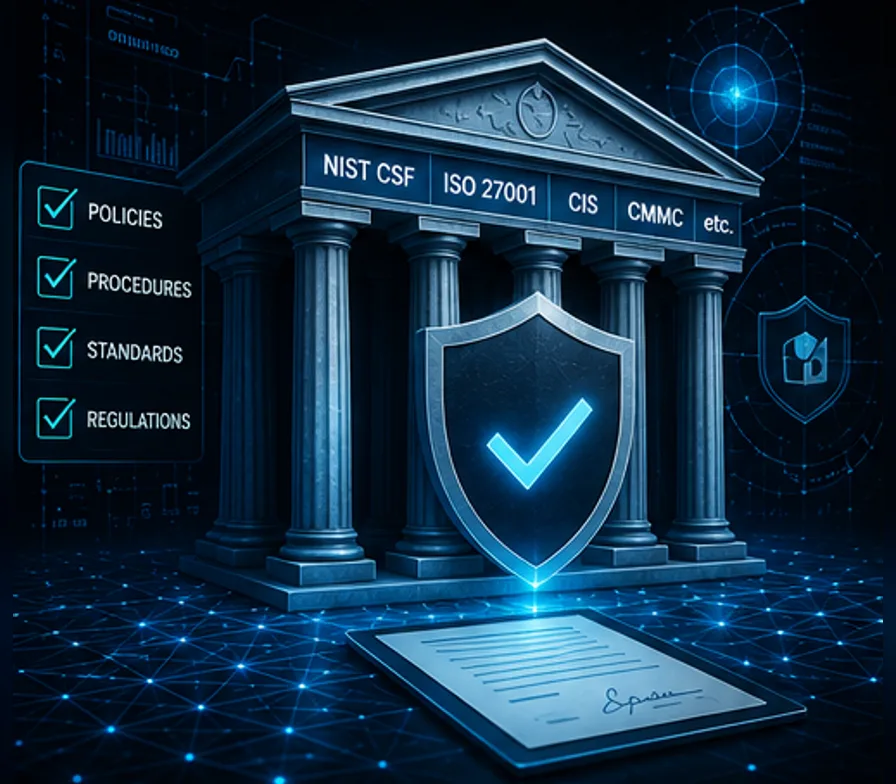
A courthouse whose columns are labeled NIST CSF, ISO 27001, CIS and CMMC, a shield carrying a check mark, a signed document, and a checklist reading policies, procedures, standards, regulations

Governance & compliance

  • Unified control framework: 201 harmonized controls across 17 domains and 6 security functions
  • A single assessment maps to 9 frameworks at once — NIST CSF, ISO 27001, CIS, CMMC, and more
  • Control-by-control maturity rating with remediation guidance attached
  • Automated policy generation, with companion standards and procedures
  • Regulatory obligation and document tracking
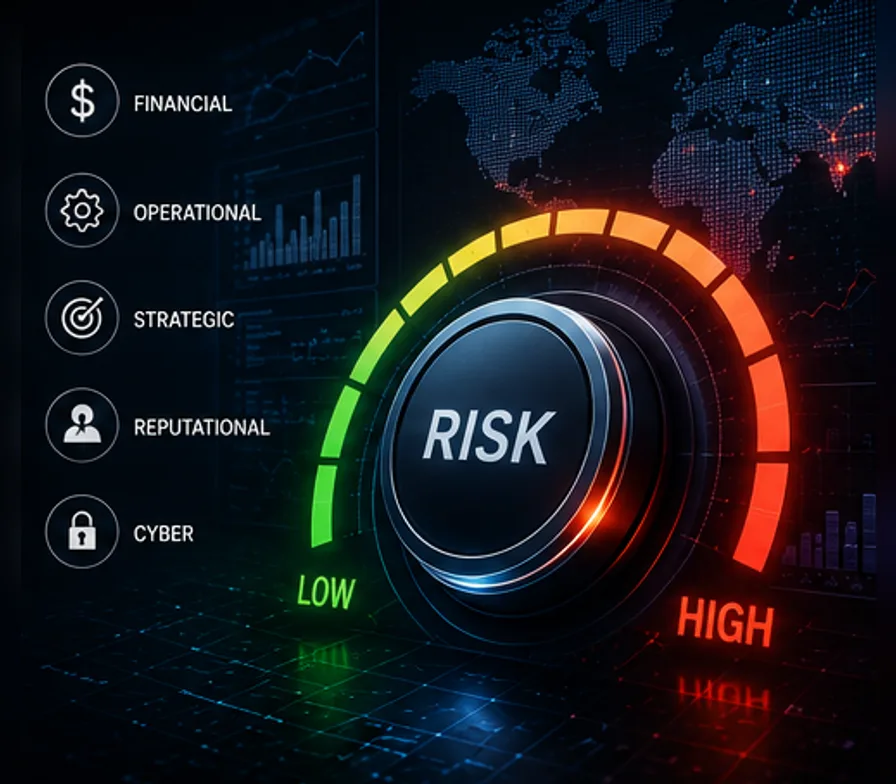
A dial labeled RISK sweeping from low to high across a green-to-red scale, beside a legend reading financial, operational, strategic, reputational and cyber

Risk management

  • Financially quantified risk analysis (FAIR-based) — gaps expressed in dollars
  • Scope builder for defining and managing assessment boundaries
  • Business impact analysis with per-asset RTO/RPO and recovery posture
  • Cyber insurance premium calculation support
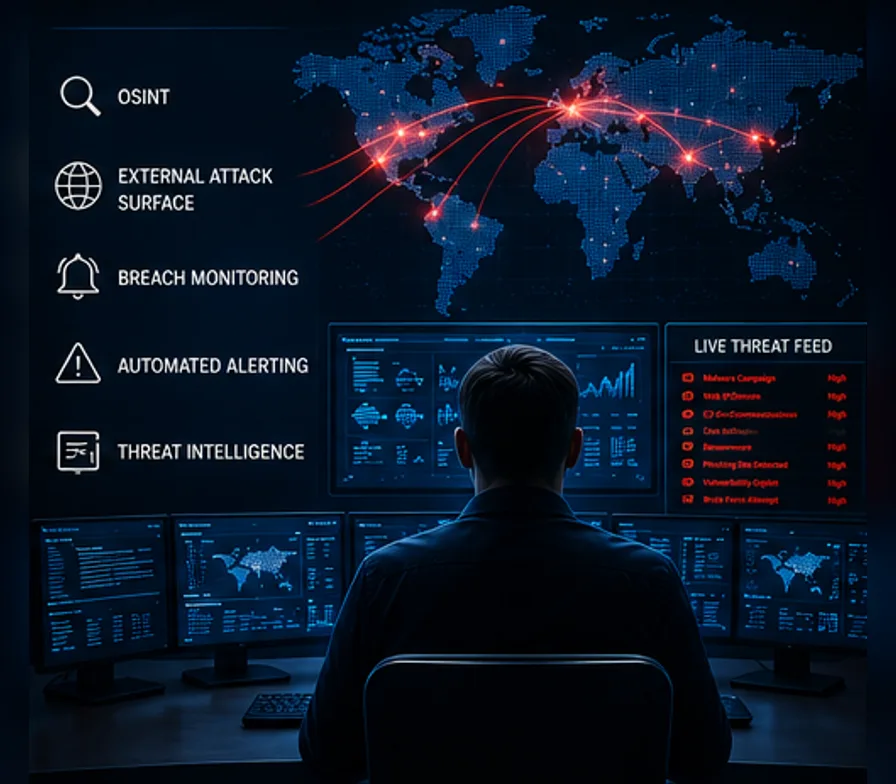
An analyst in a dark operations center facing a world map of live attack paths and a threat feed, beside a legend reading OSINT, external attack surface, breach monitoring, automated alerting and threat intelligence

Threat & exposure monitoring

  • Continuous threat exposure monitoring, read in your organizational context
  • OSINT scanning and external attack surface discovery (Nmap, WHOIS ingestion)
  • Have I Been Pwned breach monitoring with automated alerting
  • Live security news and CISA advisory feeds, deduplicated
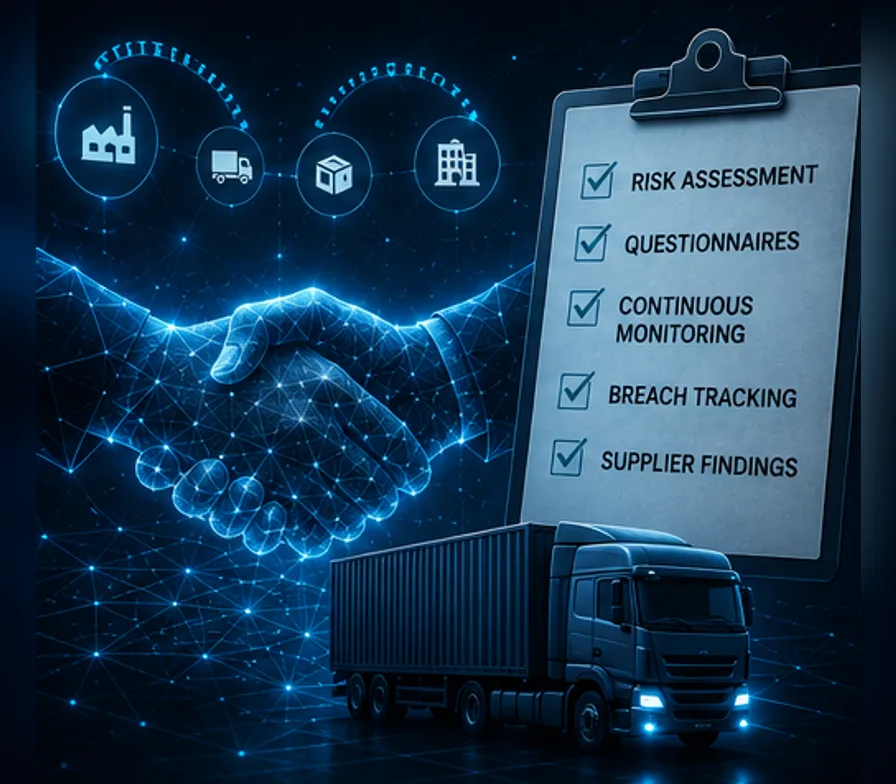
A wireframe handshake and a freight truck beneath supplier icons, beside a clipboard reading risk assessment, questionnaires, continuous monitoring, breach tracking and supplier findings

Third-party & supplier risk

  • Supplier risk assessments and questionnaires with autosave
  • Continuous supplier monitoring — breach counts and profile tracking
  • Assessment-to-ticket conversion for supplier findings
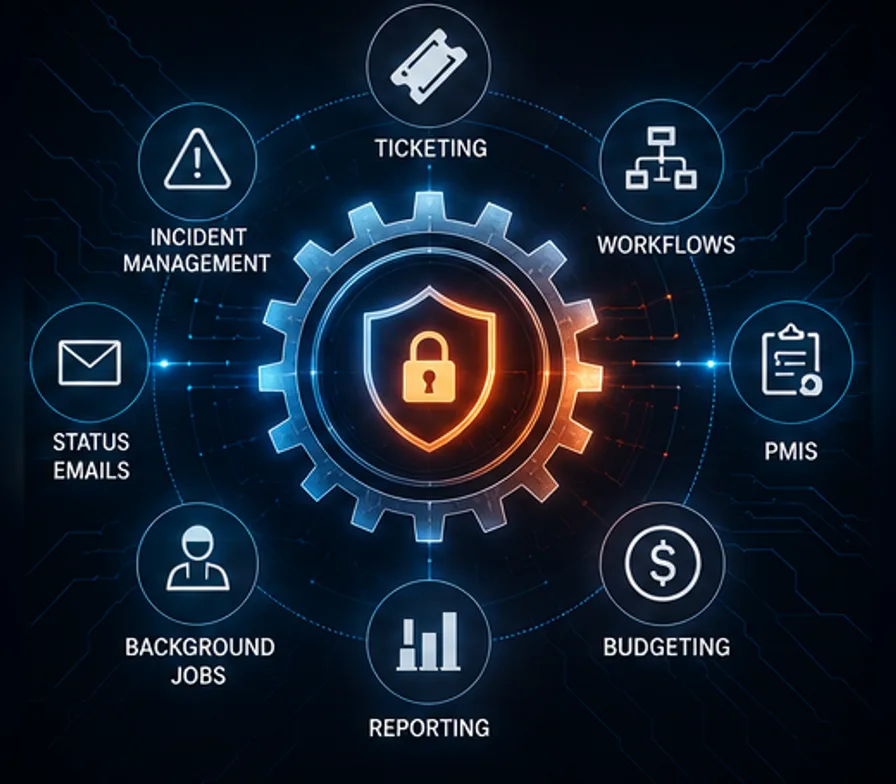
A gear enclosing a padlocked shield, ringed by labels for ticketing, workflows, PMIS, budgeting, reporting, background jobs, status emails and incident management

Operations & service management

  • Cybersecurity service management: ticketing, incident management, workflows
  • Project management (PMIS) with PERT/WBS and earned value
  • Cyber budgeting and time tracking with rate-based costing
  • Status report emails and scheduled background jobs
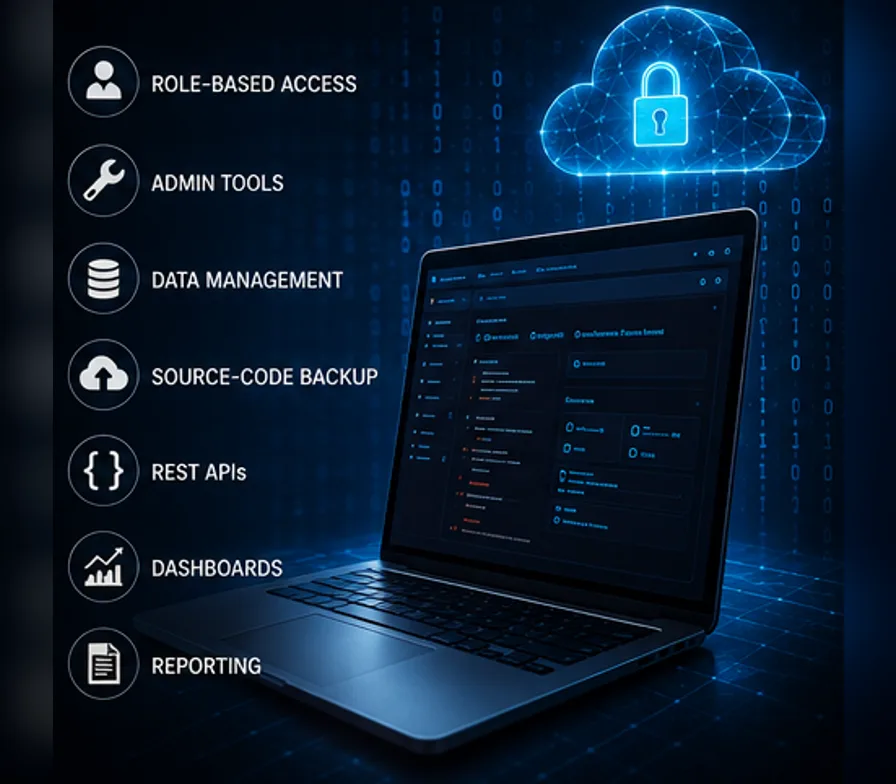
A laptop showing a platform dashboard beneath a padlocked cloud, beside a legend reading role-based access, admin tools, data management, source-code backup, REST APIs, dashboards and reporting

Platform & administration

  • Role-based access with organization-level scoping and branding inheritance
  • Admin tooling: data management, source-code backup, batch process monitoring
  • REST APIs with a Swagger explorer, health checks, and full audit logging
  • Interactive dashboards, organization mapping, and executive reporting

A security organization that does not just prove compliance when asked, but demonstrably reduces risk every day — with the financial visibility to show how much.

That is not meeting GRC requirements. That is making them the floor instead of the ceiling.

05

Capabilities

What we bring
to every engagement.

Our engagements run on a purpose-built methodology stack that standardizes evidence, accelerates assessments, and produces audit-grade deliverables. No shared drives, no screenshot-and-hope, no reinventing the spreadsheet for every client.

Risk assessment & GRC

Maturity-rated assessments, risk registers, compliance tracking, and audit management against a unified control library.

Evidence & chain of custody

Every artifact cataloged, timestamped, and mapped to the controls it satisfies — defensible under audit.

Policy lifecycle

Policy libraries designed, versioned, and maintained — with acknowledgment tracking and renewal cycles.

Vulnerability management

Program stand-up and oversight integrating enterprise scanners into a risk-scored remediation workflow.

Tabletop exercises

Industry-tailored incident scenarios with injects, participant tracking, and post-exercise after-action reports.

Attack surface review

External exposure reporting — open ports, exposed services, certificate hygiene, and shadow IT discovery.

Incident management

Response playbooks, timeline documentation, communications support, and lessons-learned integration.

Board & executive reporting

Translate technical posture into business language — measured, trended, and tied to strategic priorities.

06

Industries served

Built for regulated sectors

A stethoscope resting on a circuit board lit with blue traces

Healthcare

HITRUST · HIPAA

The door of a bank vault, its two combination dials in close view

Financial Services

FFIEC · FDIC

A manual gear selector in a car console, its shift pattern in relief

Automotive

TISAX · CMMC

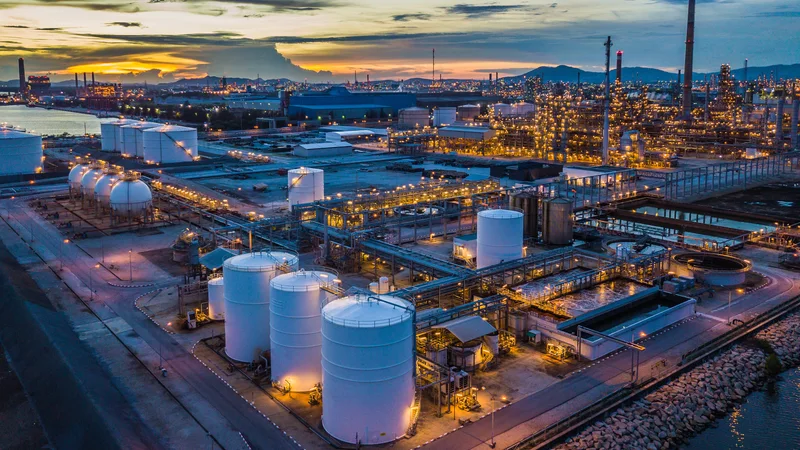
A refinery and tank farm lit up at dusk, seen from the air

Industrial & Critical Infrastructure

NIST · IEC 62443

A student in glasses reaching toward a lit wall of learning data

Education

FERPA · GLBA

The dome of the United States Capitol under a bright sky

State & Federal Government

FedRAMP · CMMC

Two utility workers in hard hats and hi-vis looking up at transmission towers at dusk

Energy & Utilities

NERC CIP

07

In the field

What it looks like in practice

Regional health system

HITRUST readiness reached in one pass

One assessment pass produced HITRUST, HIPAA, and NIST evidence at once — no three separate audits.

Three frameworks, one evidence set

Community bank

FFIEC examination passed clean

Gap remediation and board reporting turned a stressful annual exam into a formality.

No repeat findings at exam

Automotive supplier

CMMC Level 2 gaps closed on the deal clock

A prioritized remediation plan cleared the controls blocking a defense-sector contract.

Contract award unblocked
08

Engagement model

From kickoff to board readout in six weeks

Week 1

Discovery

Scope the environment, obligations, and the frameworks that actually apply to you.

Week 2

Assessment

Evidence-based control review run through our platform, answering every applicable framework in one pass.

Weeks 3–4

Analysis & quantification

Findings ranked by business risk, with the material gaps quantified in dollars.

Week 5

Roadmap

A sequenced, costed remediation plan your team and board can act on.

Week 6

Board-ready readout

An executive briefing that translates security posture into business terms.

09

Why this practice

What sets the work apart

Three frameworks, one pass

One control, mapped once, satisfies NIST, ISO, and CIS together — compliance that compounds instead of repeating.

Risk in dollars, not colors

Control gaps are quantified with a defensible, financially grounded method, so investment gets argued the way every other capital decision does.

A practicing vCISO, not a report

You get an accountable security leader in your meetings — not a PDF and a handshake.

Board-ready by default

Every engagement ends in reporting a board can read and a roadmap a team can execute.

10

Engage

Start with a complimentary pre-assessment.

Every meaningful engagement begins with a short diagnostic. Share a few details about your organization and current posture — we will respond within two business days with a no-cost briefing and a scoped path forward tailored to your environment, regulatory exposure, and priorities.

01About your organization
02Your information
03Pre-assessment diagnostic
Which frameworks are you currently aligned to? (select all that apply)
Current security leadership model *

Your information is held in confidence. Submitted details are used solely to prepare your pre-assessment briefing and are never shared with third parties.

Complimentary pre-assessment

What you will receive

  • 30-minute scoping briefing with a practicing vCISO
  • Initial control-gap and framework-alignment read
  • Regulatory exposure summary for your industry
  • Scoped engagement proposal — no obligation

Direct contact · Practice lead

Bill Leach Jr.

Managing Director of Cybersecurity, Network & Infrastructure · Practicing Virtual CISO